


Instant Download CompTIA : CS0-001 Questions & Answers as PDF & Test Engine

Updated: Nov 16, 2026
No. of Questions: 458 Questions & Answers with Testing Engine
Download Limit: Unlimited
Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
100% Money Back Guarantee
ActualVCE has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best exam practice material
- Three formats are optional
- 10 years of excellence
- 365 Days Free Updates
- Learn anywhere, anytime
- 100% Safe shopping experience
Efficiency is the quiet superpower of well-prepared candidates. The 458 practice questions for the CS0-001 exam from ActualVCE cover the knowledge points comprehensively, so your study hours go exactly where the CompTIA Cybersecurity Analyst (CySA+) Certification exam looks.
CompTIA CS0-001 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Cyber Incident Response | 31% | - Incident Handling
|
| Vulnerability Management | 26% | - Vulnerability Identification
|
| Security Architecture and Tool Sets | 16% | - Security Controls
|
| Threat Management | 27% | - Threat Intelligence
|
CS0-001 Exam FAQ: What Candidates Really Want to Know
The CompTIA Cybersecurity Analyst (CySA+) Certification exam runs 165 minutes and contains 85 (maximum) questions. That ratio is the real exam challenge: knowing the content is necessary, but pacing is what finishes it. Rehearse with full-length timed sessions in the ActualVCE test engine, and treat your pacing plan as seriously as your study plan.
Yes — ActualVCE provides a free demo of the CompTIA Cybersecurity Analyst (CySA+) Certification questions and answers, available for download as a reference before you decide. After purchase, 365 days of free updates are included; once the year ends, you can extend the update service at a 50% discount from your member zone.
Delivery is quick and easy: two steps finish your order, and your CS0-001 product is emailed to your mailbox within one minute of payment — then just download the attachment. If nothing arrives within 2 hours, check spam and contact us for an immediate resend. On failure, the refund policy is specific: sit the corresponding CS0-001 exam within 60 days of purchase, and a fail qualifies you for a full refund — submit a scanned enrollment slip and the official Score Report PDF within 2 days after the exam, and the refund completes within 7 days. Excluded: attempts within 3 days of purchase, exams never actually taken, free materials, and expired orders — the candidate name must also match the payer name. Prefer to continue studying? Exchange your product for two free exam products of equal value, with update service kept on the original purchase.
No formal prerequisite. CompTIA recommends Network+, Security+ or equivalent knowledge and 3-4 years of hands-on information security experience. These rules are set by CompTIA and can change, so confirm the current requirements on the official exam page: https://www.comptia.org/certifications/cybersecurity-analyst before registering for the CompTIA Cybersecurity Analyst (CySA+) Certification exam.
The CS0-001 exam is CompTIA's official certification test, and passing it awards the CSA+ credential — a certification at the Intermediate / Professional level. Its career value is simple: certified professionals are the first shortlisted for better roles and promotions, which is why candidate numbers keep climbing. It also connects to CompTIA Security+, CompTIA PenTest+, CompTIA CASP+, extending its value across a wider credential path.
The CompTIA Cybersecurity Analyst (CySA+) Certification syllabus spans 4 knowledge areas. The heaviest are Threat Management (27%), Security Architecture and Tool Sets (16%), Cyber Incident Response (31%). Match your study time to those weights — the full outline is listed in the section above.
Each CompTIA Cybersecurity Analyst (CySA+) Certification attempt costs USD 349, and the pass mark is 750 (on a scale of 100-900). A retake bills the full fee again, so the financially smart move is arriving overprepared. Use ActualVCE practice questions until your timed scores clear 750 (on a scale of 100-900) comfortably, then book the CS0-001 exam once.
CompTIA Cybersecurity Analyst (CySA+) Certification Sample Questions:
Organizational policies require vulnerability remediation on severity 7 or greater within one week. Anything with a severity less than 7 must be remediated within 30 days. The organization also requires security teams to investigate the details of a vulnerability before performing any remediation. If the investigation determines the finding is a false positive, no remediation is performed and the vulnerability scanner configuration is updates to omit the false positive from future scans:
The organization has three Apache web servers: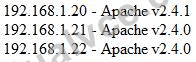
The results of a recent vulnerability scan are shown below: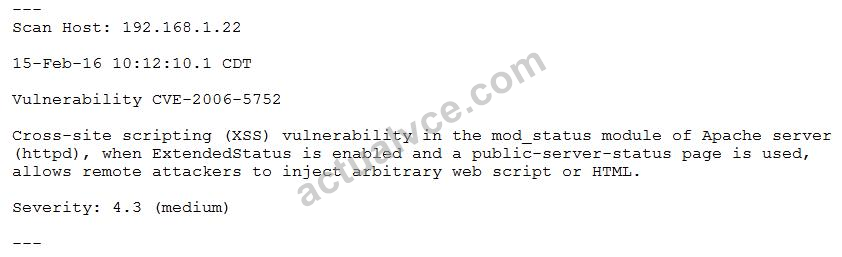
The team performs some investigation and finds a statement from Apache: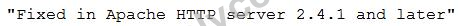
Which of the following actions should the security team perform?
- A. Investigate the false negative on 192.168.1.20
- B. Remediate 192.168.1.20 within 30 days
- C. Ignore the false positive on 192.168.1.22
- D. Remediate 192.168.1.22 within 30 days
Correct Answer: D 🗳️
A vulnerability scan returned the following results for a web server that hosts multiple wiki sites:
Apache-HTTPD-cve-2014-023: Apache HTTPD: mod_cgid denial of service CVE-2014-0231 Due to a flaw found in mog_cgid, a server using mod_cgid to host CGI scripts could be vulnerable to a DoS attack caused by a remote attacker who is exploiting a weakness in non-standard input, causing processes to hang indefinitely.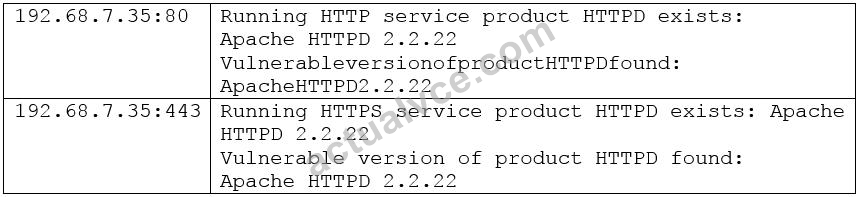
The security analyst has confirmed the server hosts standard CGI scripts for the wiki sites, does not have mod_cgid installed, is running Apache 2.2.22, and is not behind a WAF. The server is located in the DMZ, and the purpose of the server is to allow customers to add entries into a publicly accessible database.
Which of the following would be the MOST efficient way to address this finding?
- A. Upgrade to the newest version of Apache.
- B. Disable the HTTP service and use only HTTPS to access the server.
- C. Document the finding as a false positive.
- D. Place the server behind a WAF to prevent DoS attacks from occurring.
Correct Answer: C 🗳️
A cybersecurity analyst is reviewing log data and sees the output below: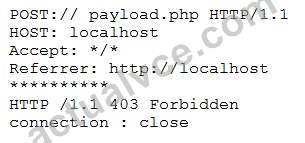
Which of the following technologies MOST likely generated this log?
- A. Network-based intrusion detection system
- B. Web application firewall
- C. Stateful inspection firewall
- D. Host-based intrusion detection system
Correct Answer: B 🗳️
A technician receives the following security alert from the firewall's automated system: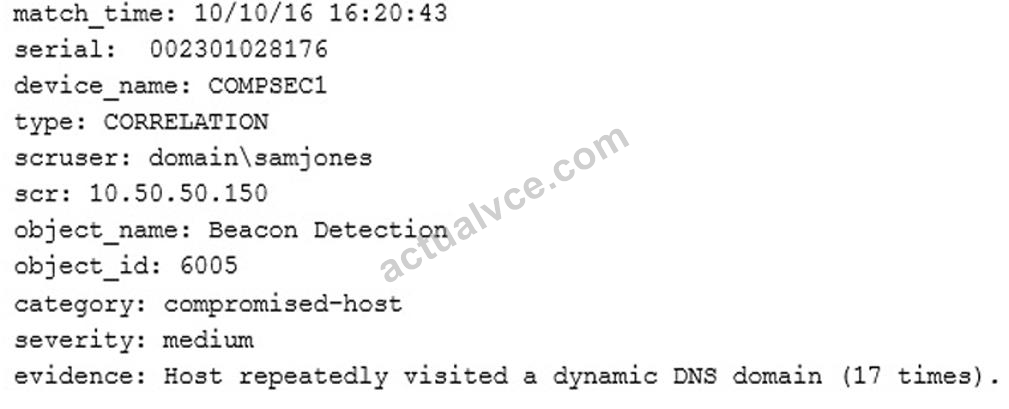
After reviewing the alert, which of the following is the BEST analysis?
- A. This alert indicates an endpoint may be infected and is potentially contacting a suspect host.
- B. This alert was generated by the SIEM because the user attempted too many invalid login attempts.
- C. This alert indicates a user was attempting to bypass security measures using dynamic DNS.
- D. This alert is a false positive because DNS is a normal network function.
Correct Answer: A 🗳️
A cybersecurity consultant found common vulnerabilities across the following services used by multiple servers at an organization: VPN, SSH, and HTTPS. Which of the following is the MOST likely reason for the discovered vulnerabilities?
- A. Weak level of encryption entropy
- B. Vulnerable implementation of PEAP
- C. Vulnerable version of OpenSSL
- D. Leaked PKI private key
- E. Common initialization vector
Correct Answer: A 🗳️
Viewing page 1 out of 92 pages.
Viewing questions 1-5 out of 458 questions.
 1135 Customer ReviewsCustomers Feedback (* Some similar or old comments have been hidden.)
I just took my CompTIA certification testing for CS0-001 exam and passed CS0-001 with full score.
Anna

Passed CompTIA CS0-001 yesterday, Dump 100% valid.I would appreciate a valid dump.
Ivan
so unexpected, i have passed CS0-001 exam test with your study material , i will choose ActualVCE next time for another exam test.
Sylvia
Thank you, ActualVCE! I just passed CS0-001 exam, now i cant wait to get more certifications.
Irma
The knowledge contained in this CS0-001 training dump is complete and easy to learn. I feel grateful to buy it. Nice purchase!
Donna
Cheers! I finally passed the exam. Truly, the CS0-001 exam dump was very much helpful as I got so many questions common.
Isabel
It was nothing less than a dream comes true when I saw a handsome job opportunity requiring fresh certified persons to apply. I turned out to ActualVCE relying on his previous popularity and it really proved nothing less than a miracle to get me t
Richard

These CS0-001 dumps worked fine for me. There were a lot of questions from them on the exam too. I passed today.
Cyril
This exam is pretty easy with the help of the CS0-001 exam questions. Especially when compared to the other two exams which i have passed with more practice questions. Thanks for the support!
Nat
93% is my final score.
Rachel
I passed CS0-001 exams on the first try. You helped me a lot. I am especially pleased with your practice tests which are excellent study materials. Thank you, ActualVCE!
Heloise
Keep up the good work!!!!!!!!!!!!!!
I just took my CS0-001 exam and passed with a good score!
Anna
I will suggest you to take CS0-001 practice dumps before appearing for the exam. They really help preparing for actual exam!
Maria
CS0-001 test materials are valid, and they helped me pass the exam in my first attempt, thank you very much!
Lennon
The CS0-001 eaxm material is authentic and the way the course is designed highly convenient. It really helpful, I passed in a short time.
Ed
I passed my exam and received my badge thanks to CS0-001 Exam Dumps from ActualVCE.
Meredith
Passed Exam CS0-001 without any hassle!
Best Solution for Passing CS0-001 Exam!!!
Hale
Instant Download CS0-001
After Payment, our system will send you the products you purchase in mailbox in a minute after payment. If not received within 2 hours, please contact us.
365 Days Free Updates
Free update is available within 365 days after your purchase. After 365 days, you will get 50% discounts for updating.

Money Back Guarantee
Full refund if you fail the corresponding exam in 60 days after purchasing. And Free get any another product.
Security & Privacy
We respect customer privacy. We use McAfee's security service to provide you with utmost security for your personal information & peace of mind.
Related Exams
Security & Privacy
ActualVCE respect customer privacy. We use McAfee's security service to provide you with utmost security for your personal information & peace of mind.
Instant Download
After Payment, our system will send you the products you purchase in mailbox in a minute after payment. If not received within 2 hours, please contact ActualVCE.
365 Days Free Updates
Free update is available within 365 days after your purchase. After 365 days, you will get 50% discounts for updating.
Try Before Buy
ActualVCE offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.
